
 Am I Being Pwned
See every browser extension on your SentinelOne® fleet.
SentinelOne sees every process on your endpoints, but it does not see the extensions running inside the browser. Below is everything this integration reads from and writes to your console, with the permission each part uses.
Connecting deploys nothing to your endpoints
Top to bottom: Am I Being Pwned, SentinelOne, your fleet
- Agent list
- Extension inventory
- Risk alerts
- Indicators
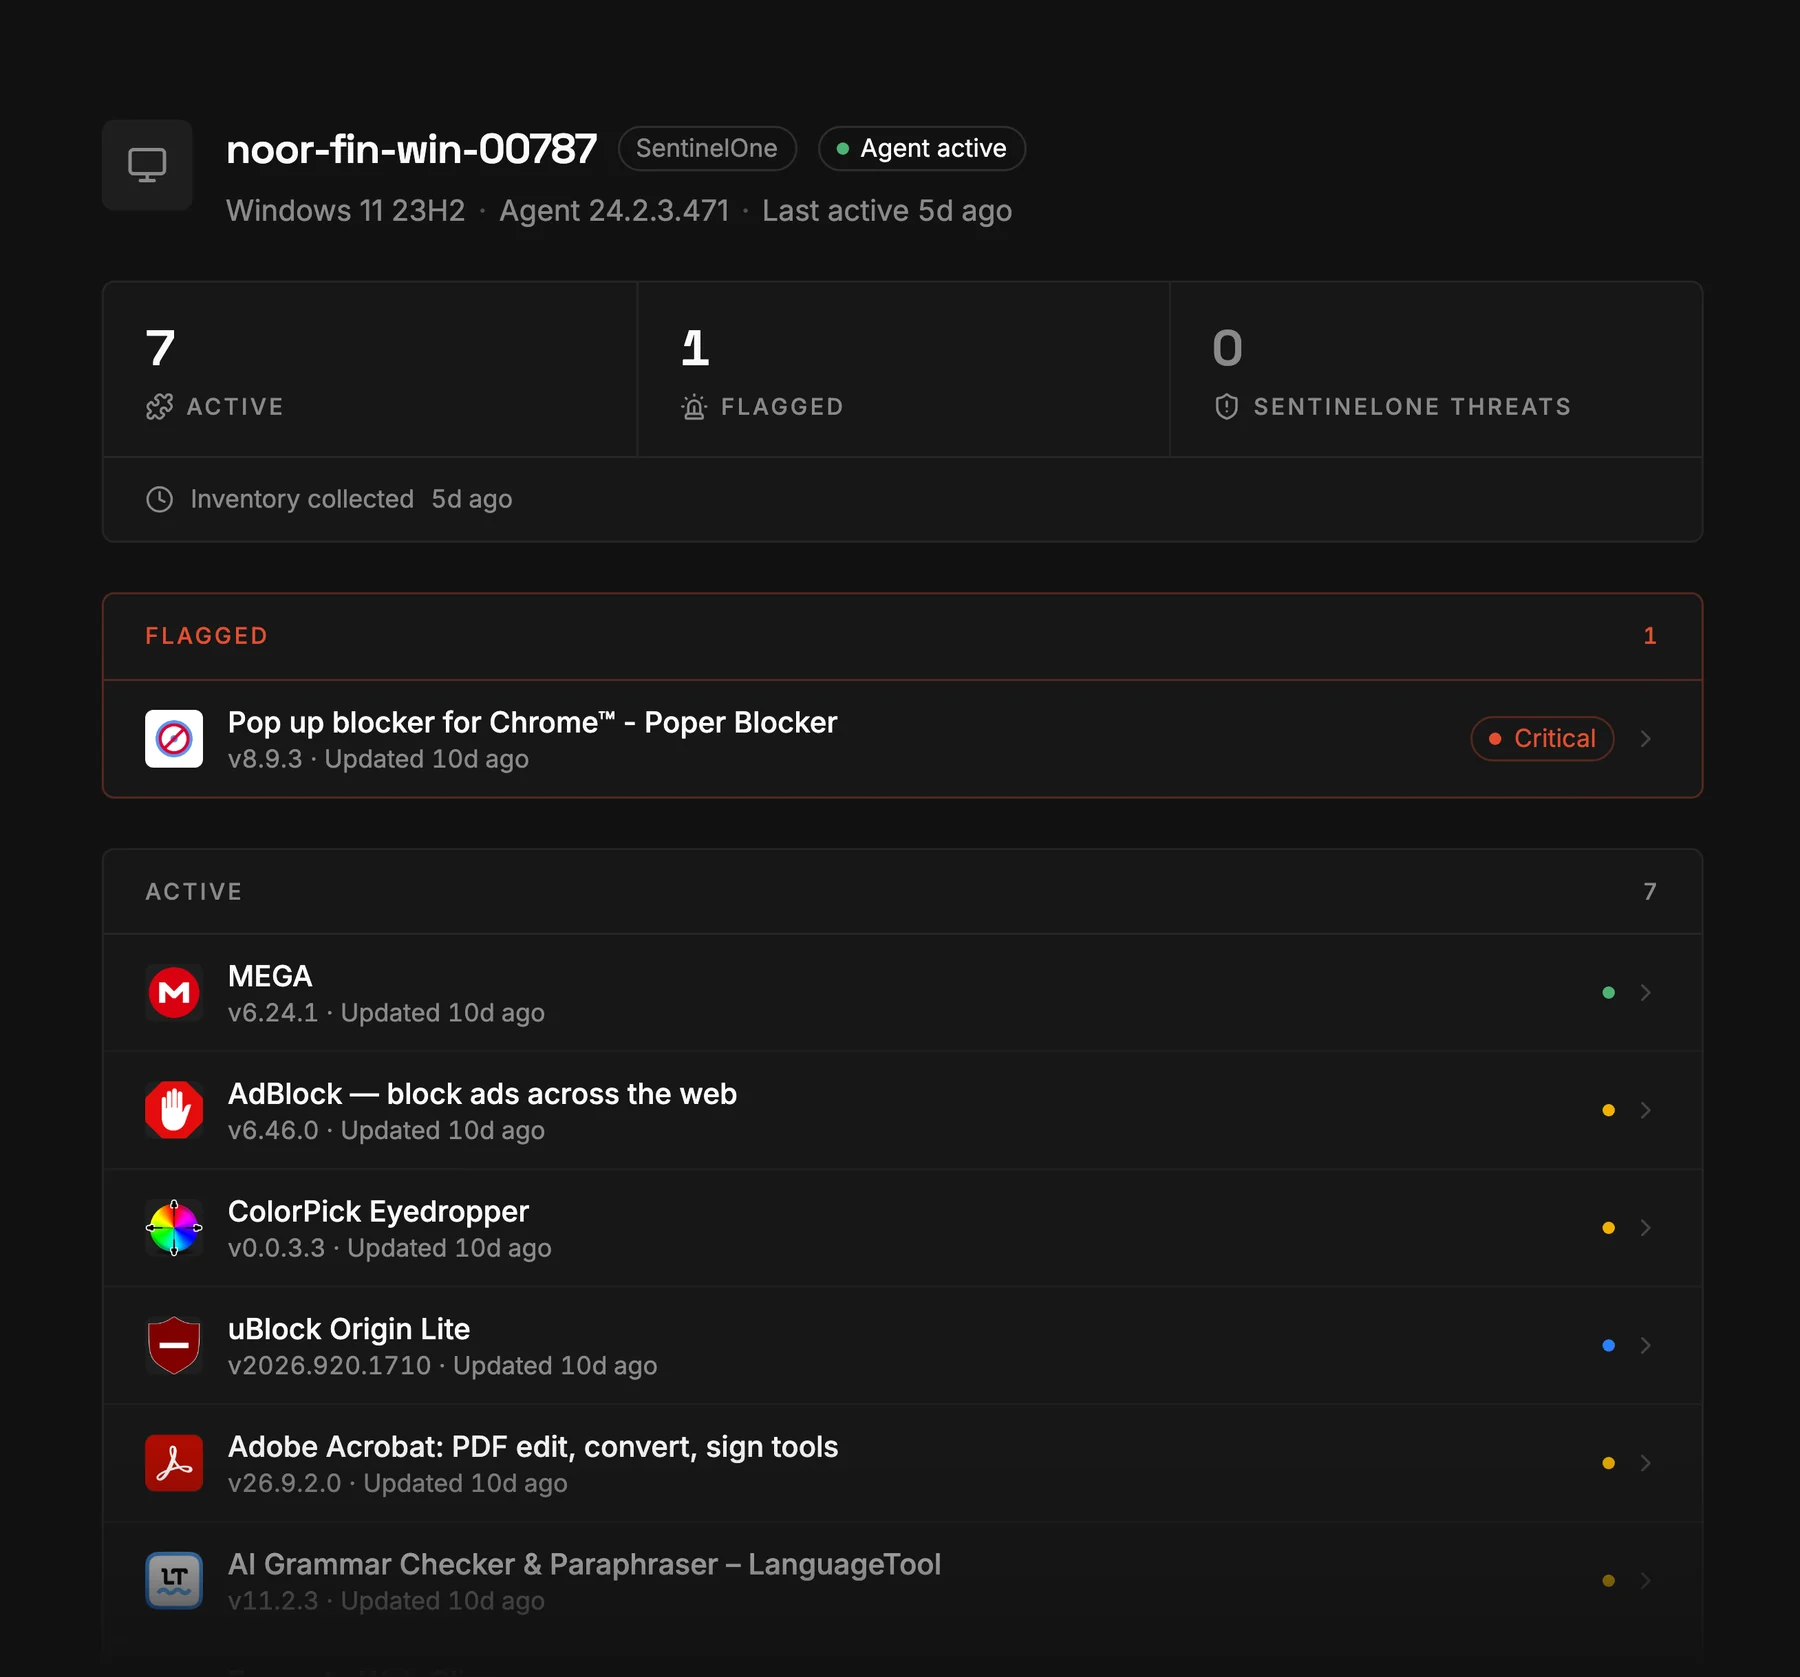
Each SentinelOne agent, with its extensions.
Every agent appears as a device with its extensions listed and flagged ones at the top. Search for an extension to see every device that has it.
Console writes
What we write into your SentinelOne console.
Indicators start on the first sync. Alert rules start when you turn on risk sync. Both are tagged with our source, and disconnecting removes them.
Risks synced to your console
Each risk open on your fleet becomes a STAR custom rule in your console. The rule fires when an endpoint touches that extension's files, and the alert names the machine. By default they cover high severity and above, and they only alert. When you resolve the risk in our dashboard, we delete the rule on the next sync.
- AIBP: Free VPN ProxyFIN-LT-0142, STAR custom rule2 min ago
- AIBP: PDF ToolkitENG-MBP-0087, STAR custom rule1 hr ago
- AIBP: Cookie ManagerHR-LT-0051, STAR custom ruleYesterday
Indicators in Threat Intelligence
Extensions on your fleet that we rate malicious, high or critical go into Threat Intelligence as indicators, one per extension, tagged with our source. Each one expires after 90 days unless a sync renews it. If we downgrade an extension we withdraw its indicator, and disconnecting withdraws them all.
- Type
- URL
- Value
- chromewebstore.google.com/detail/…
- Name
- PDF Toolkit (high)
- Source
- Am I Being Pwned
- Valid until
- 90 days, renewed each sync
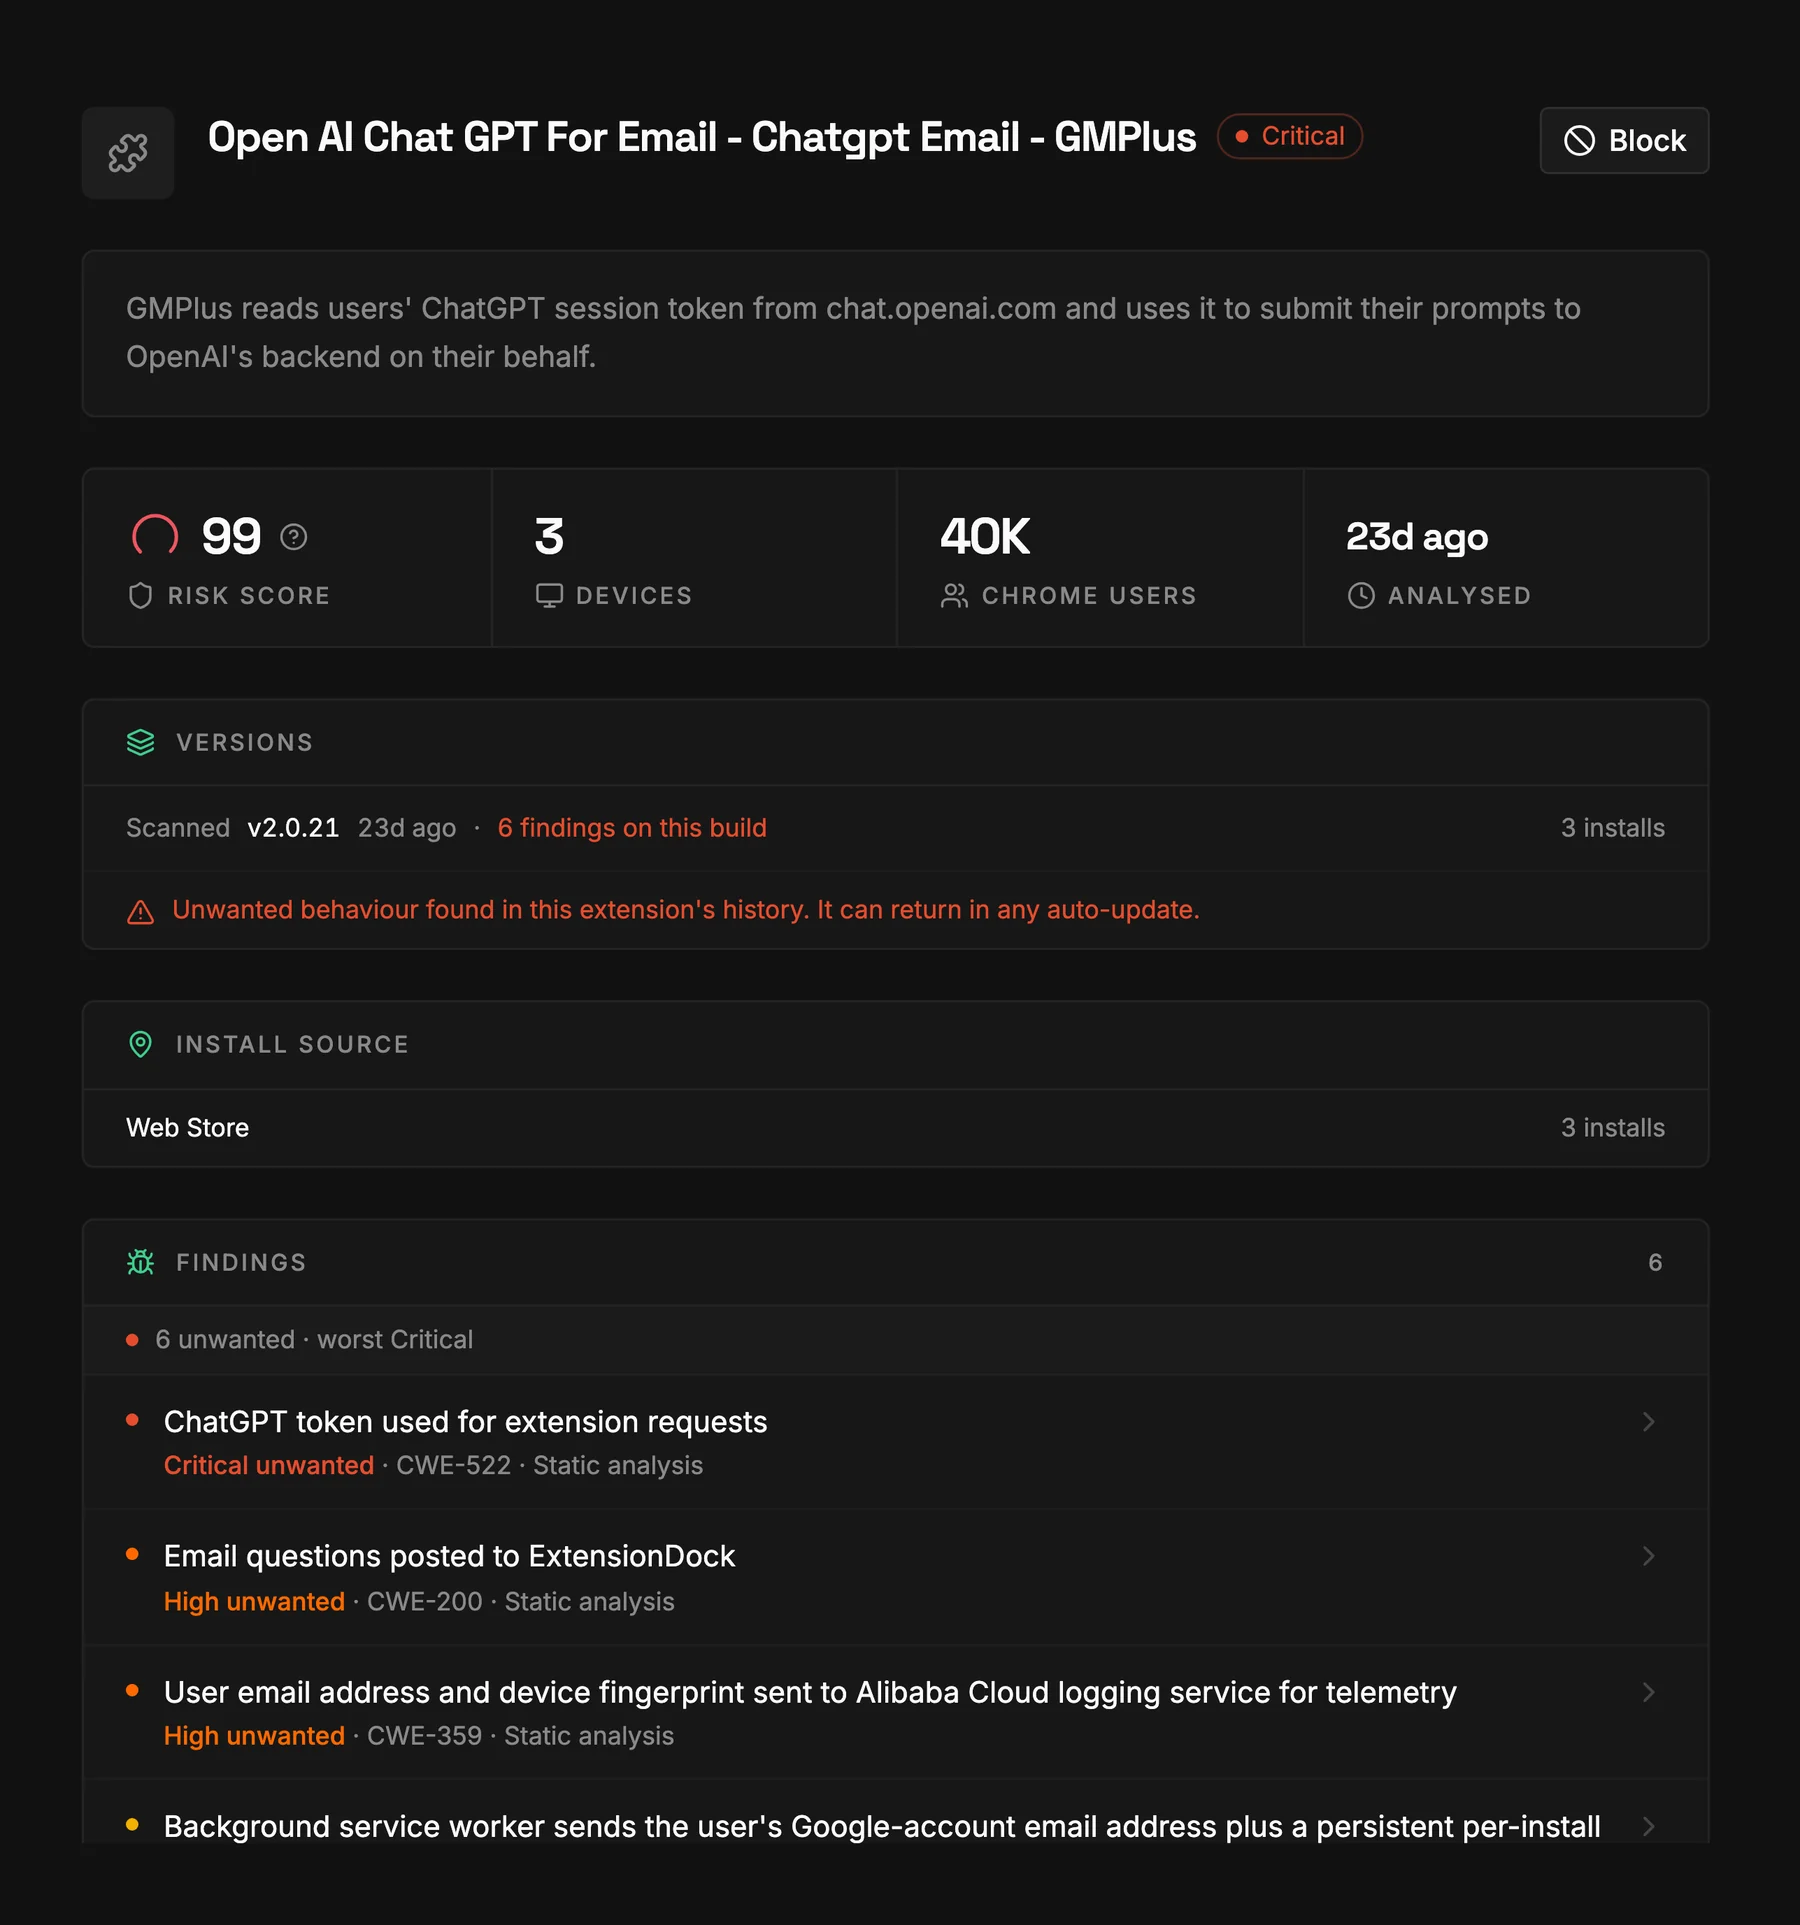
The evidence behind each verdict
Each flagged extension lists the findings that produced its verdict, taken from the version on your fleet, so your team does not have to redo the analysis.
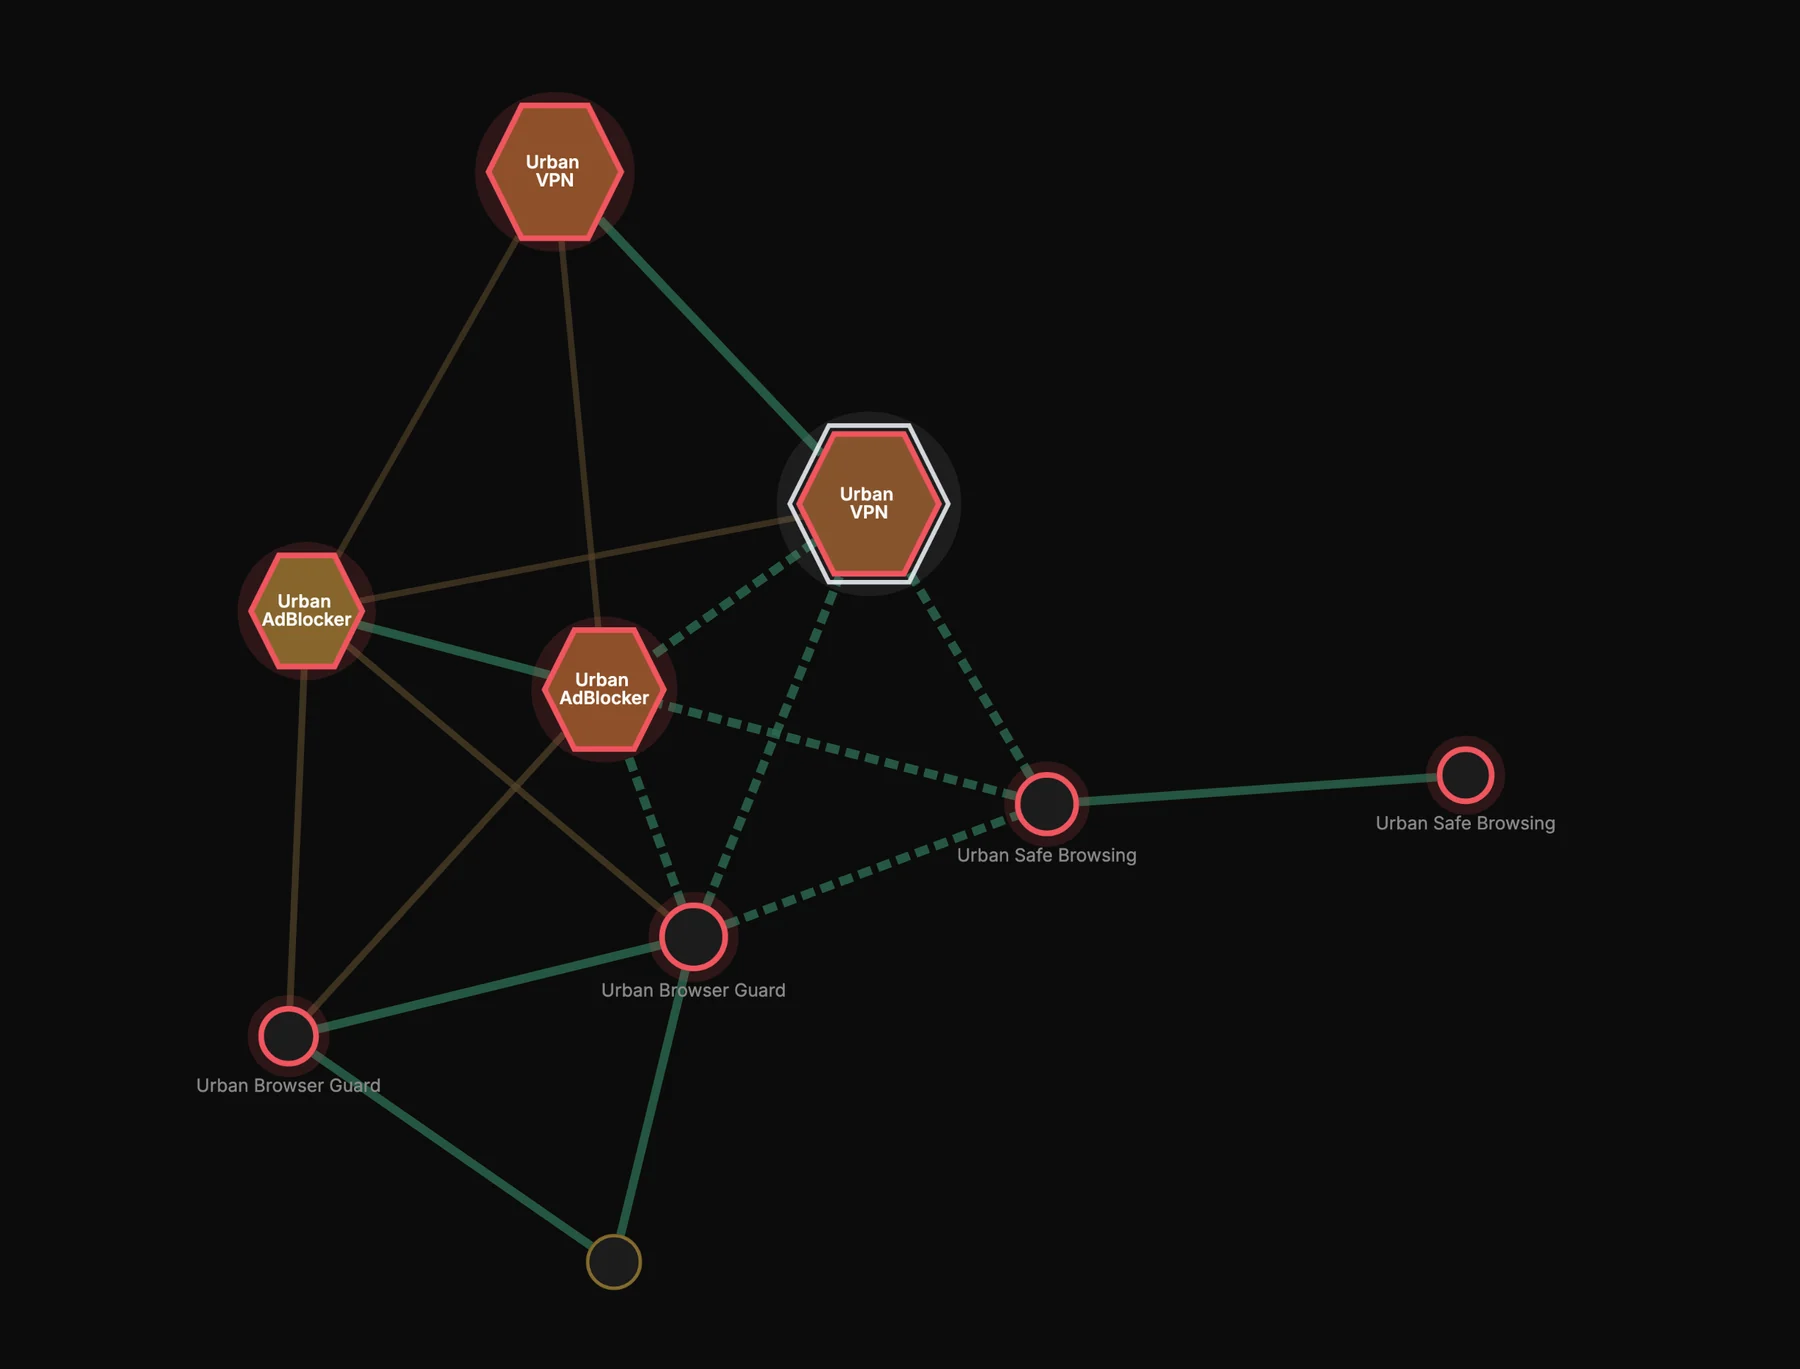
Related extensions
The graph links extensions that share code, infrastructure or accounts. Start from one flagged extension to see the related ones on your fleet.
The role
The permissions we ask for.
This is the custom role you create in SentinelOne. Ticked boxes are required, dashed boxes depend on what you turn on, and everything else stays off. File Fetch is the only endpoint action, and only if you collect inventory with it.
To remove our access, disconnect in our dashboard and we delete the token, or delete the Service User in SentinelOne and the token stops working at once.
- View
- File Fetchfor File Fetch inventory
- Every other endpoint actionisolate, reboot, scan, quarantine
- Viewfor File Fetch inventory
- View
- Managefor indicators
- Viewgranted automatically
- View and Managefor risk sync
Inventory
Four ways to collect extension inventory.
File Fetch is the default when your license includes it and needs nothing deployed. Our collector does the same job on a narrower role. Both are compared below.

File Fetch
Nothing to deployOnce a day we ask each agent for its browser settings files through SentinelOne's File Fetch, and read the extension list out of them. Nothing runs on the endpoint beyond the agent's own upload.
- Credentials we hold
- A Service User token on the role above, with Endpoints File Fetch and Activity View added
- Worst case if we are breached
- Someone fetches files from your endpoints, each one logged in your console, or writes alert rules and indicators into it
- Profiles read
- One user's browser profiles per device, the last signed in
- SentinelOne license
- Singularity Complete or higher, which include File Fetch
Our collector
Least privilegeDeploy our script like any other, on the schedule your change process sets. It reads every user profile on the machine.
- Credentials we hold
- A Service User token on the role above, plus a write-only key that can submit inventory for your org and nothing else
- Worst case if we are breached
- Someone posts false inventory, or writes alert rules and indicators into your console
- Profiles read
- Every user's browser profiles
- SentinelOne license
- Any
Google Workspace
No collectorIf you manage Chrome through Google Workspace, an admin signs in once and we read the inventory Chrome already reports, every hour. There is nothing to deploy.
How the Workspace integration worksUpload a list
No collectorUpload a CSV or spreadsheet export from any tool, or post the list to our API on a schedule. It covers Chrome and Edge and works before you deploy anything.
Setup
Setup takes about twenty minutes, mostly in your SentinelOne console.
- 01
Create a role
Use account scope and tick the boxes shown above.
- 02
Add a Service User
Assign it the role and copy its API token.
- 03
Paste the token
Paste it into our dashboard. The first sync runs straight away.
- 04
Choose an inventory source
Pick File Fetch, the collector, Google Workspace or an upload.
Security
Security review questions.
Short answers to what security teams ask about this integration.
- Can it act on our endpoints?
- Only to fetch browser files, if you use File Fetch. File Fetch is the one endpoint action in the role, and we use it to ask each agent for browser settings files. There are no other endpoint actions, so we cannot isolate, reboot, kill or quarantine anything.
- What does File Fetch read?
- Each browser's settings files, for one user per device. That is the last signed-in user. Chrome, Edge, Brave, Vivaldi and Chromium's Local State and Preferences files, Firefox's profiles.ini and extensions.json, and Safari's extension lists. SentinelOne reports no user on Linux, so there we first fetch /etc/passwd and read the first person's account. The agent locks each upload with a password we set for that request. We read the extension list out of the files in memory and keep each extension's ID, version, install type and whether it is on. The files themselves are never stored.
- Which SentinelOne license do we need?
- Singularity Complete or higher, for File Fetch. On other licenses, run our collector through Intune, Jamf, GPO or an RMM, connect Google Workspace, or upload a list as a CSV or through the API.
- What does it write into our console?
- Indicators, alert rules if you turn them on, and File Fetch requests. Indicators for extensions we have flagged start on the first sync. STAR alert rules start when you turn on risk sync. Both are tagged with our source, and disconnecting removes them. With File Fetch, each request and upload shows in your activity log, and the locked upload stays in your console like any other fetch.
- What does the collector read?
- Extension folders, and whether each extension is on. It runs as SYSTEM or root so it can see every user profile. It installs nothing and leaves nothing running. It writes nothing unless you turn on enforcement, which puts your blocklist into local browser policy. You get it as plain text, so you can check this yourself.
- How are credentials stored?
- Encrypted at rest. They sit on a database with no public network endpoint, and we never show a token back after you paste it.
- Can we revoke access without you?
- Yes. Delete the Service User in SentinelOne and its token stops working immediately. You can rotate the ingest key from the dashboard.
Hosting and the rest of our posture are on our security page. For anything your questionnaire asks that this page does not cover, ask an engineer.
Find out what is actually installed.
Connecting deploys nothing, and your agent list arrives on the first sync. Questions go to the engineers who built the integration.
SentinelOne®, Singularity™ and the SentinelOne logo are trademarks of SentinelOne, Inc. Used for identification only; this integration is built by Am I Being Pwned and is not endorsed by or affiliated with SentinelOne.