


Browser extension
Invite link or Google Admin force-install. Every extension your team runs, continuously monitored.
Search for problematic browser extensions across your fleet.
A signature scanner only finds patterns it already knows.
We read what the code actually does, every line.
This led us to:

Stylish hid behind 4 layers of base64 + AES-256-CBC + a columnar transposition cipher.
We unwrapped all of it.
Cyberhaven's attackers didn't change permissions, they changed code. We rescan every release, so a trusted extension can't quietly pivot into a stealer.
LLM pipeline catches what no signature has seen: encoded payloads assembled at runtime, weird egress, page leaks.
An agent drives the extension like a real user, with aged accounts to trigger gated behaviour.
Every outbound request, traced live

Layered defence. Every finding survives cross-examination before it ever reaches you.
Recently flagged by us
Threat Intelligence Feed
Every confirmed finding, malware in silent updates and vulnerabilities in trusted extensions, published as machine-readable threat intel your stack can ingest.
Explore the feedIndicators, malware, and relationship objects straight from the spec. No proprietary schema to map.
Findings carry ATT&CK technique and CWE IDs where mapped, so they drop straight into your existing detections.
Works with
every popular browser
The pipeline
Chrome Web Store
315K extensions
Edge Add-ons
30K extensions
Safari Extensions
12K extensions
Static Analysis
Agents read the bundle before it ever runs. Manifest, code and supply chain.
manifest.json · host_permissions · code-bundle · npm-tree · signing-cert
Dynamic Analysis
Detonated in a sandboxed browser. Every call, request and write is traced.
network.trace · dom.access · storage.io · eval.calls · exfil.detect
Agentic Verification
Multiple agents cross-check findings and reconcile them into a single claim with cited evidence.
cross-ref · dedupe · evidence-link · severity-score
Exfiltrates all URLs in real time
8M Users
Trusts main world in cryptographic operations
2M Users
Scoped to single host, no telemetry
700k Users
Deep-dives on the extensions, vendors, and attack patterns our pipeline surfaced.
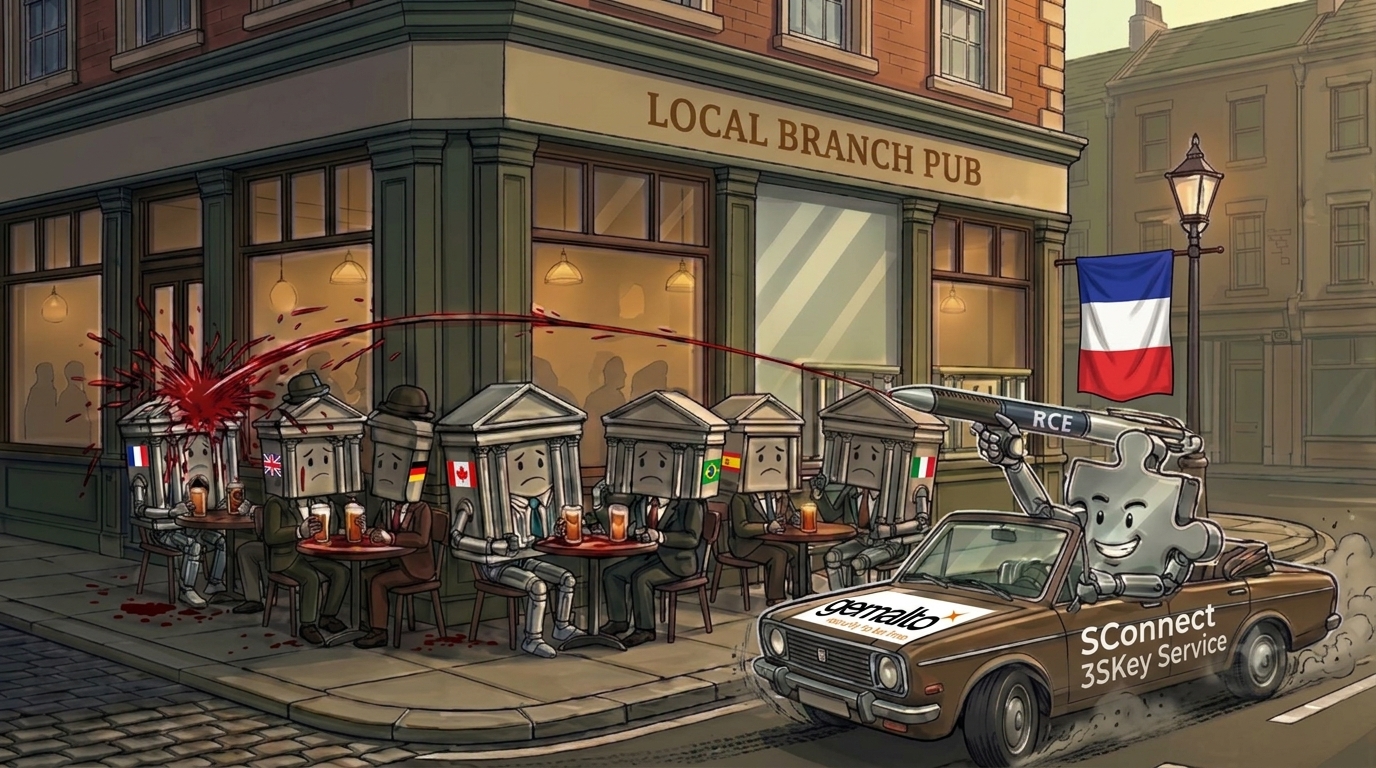
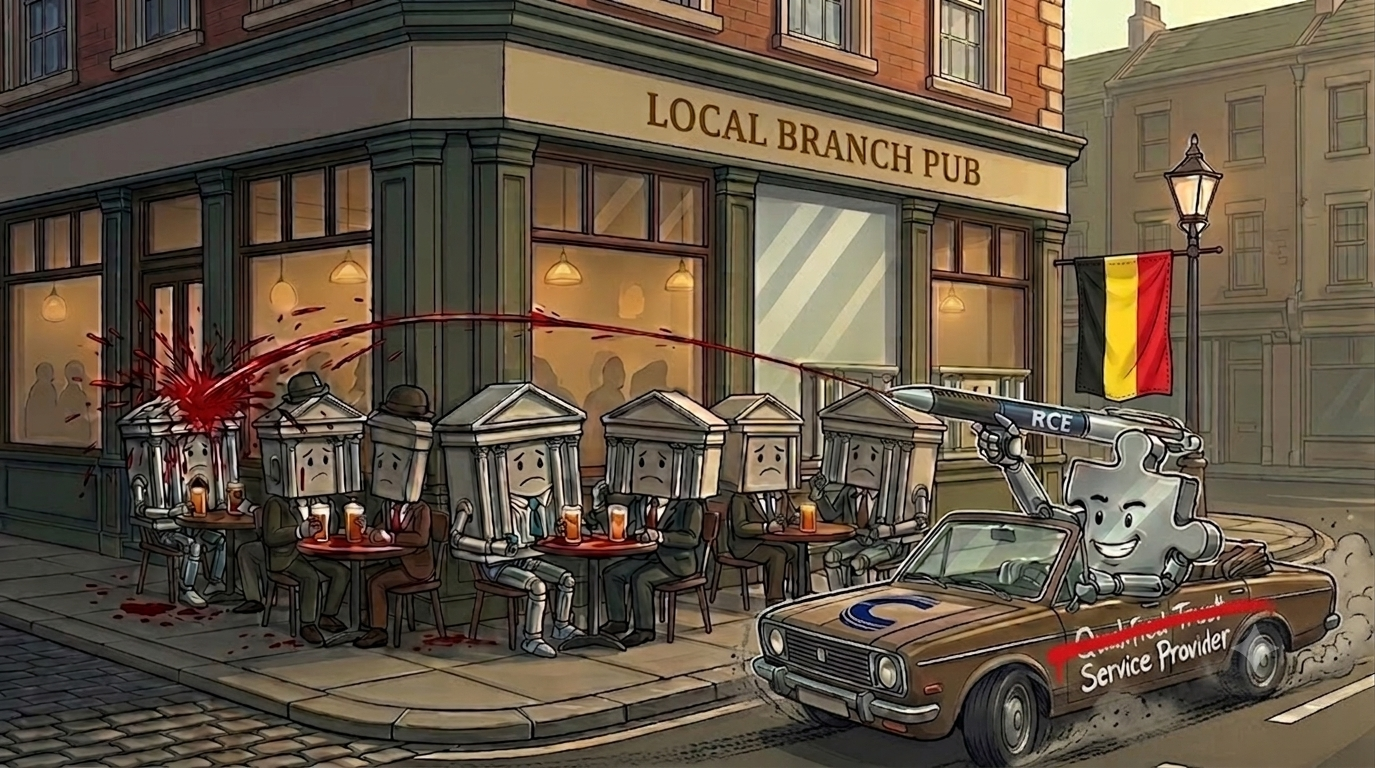
SConnect (1M+ users), the extension and native host used to authenticate with 3SKey, SWIFT, eIDs and other hardware signing tokens, had a drive-by RCE: any site or iframe could silently download and run a DLL by exploiting an uninitialised-memory bypass in its hand-rolled RSA-2048 token validation. CVE-2026-18397.
Nang
CTO, Streamable
At Streamable, we can't afford security incidents and Am I Being Pwned found problematic extensions we had installed.

Centre for Cybersecurity Belgium
Wall of Fame 2026Recognised for the responsible disclosure of critical vulnerabilities affecting users in Belgium and across the EU.
@phia
Phoebe Gates & Sophia Kianni
Am I Being Pwned made Phia more secure.
Integrations
Three ways to wire up Am I Being Pwned. Use one or all of them.
Pricing
Priced by device, with dashboard seats for your security team on every plan.
20 devices
100 devices
1,000 devices
1,000 devices, with room for 5,000.
$2,868 billed yearly. +$20 per 100 more devices
5,000+ devices
Every account starts on Free. Business and Enterprise can be tried free for 14 days from your dashboard. Invoice billing on every paid plan. Prices in USD.