Blog
Research, findings, and updates on browser extension security.
Fortinet Privileged Access Agent: Any Site Could Control Your Proxy and Watch Your Tab
The FortiPAM Chrome extension (1M+ users), used for Privileged Access Management, let any site set the browser's proxy for the session, open a new tab and stream screen recordings of it to an attacker's server. CVSS 9.1. CVE-2026-84388.
Solar Winds Part 2 Avoided: N-Able Passportal Vault Leak
N-Able's PassPortal extension, on Chrome and Edge allowed any site or iframe a user is presented with to gain complete, persisted access to the decrypted vault. CVSS 4.0, 9.4. Fixed within 24hrs. 73k+ affected weekly active users.
8 out of 10 Banks in Belgium HATE This One Weird eID RCE
The Connective signing extension, used by 8 of the 10 largest banks in Belgium and 60+ government agencies, let any website read your eID and Maestro cards, recover your eID PIN, and trigger a drive-by RCE. All the victim sees is a file download.
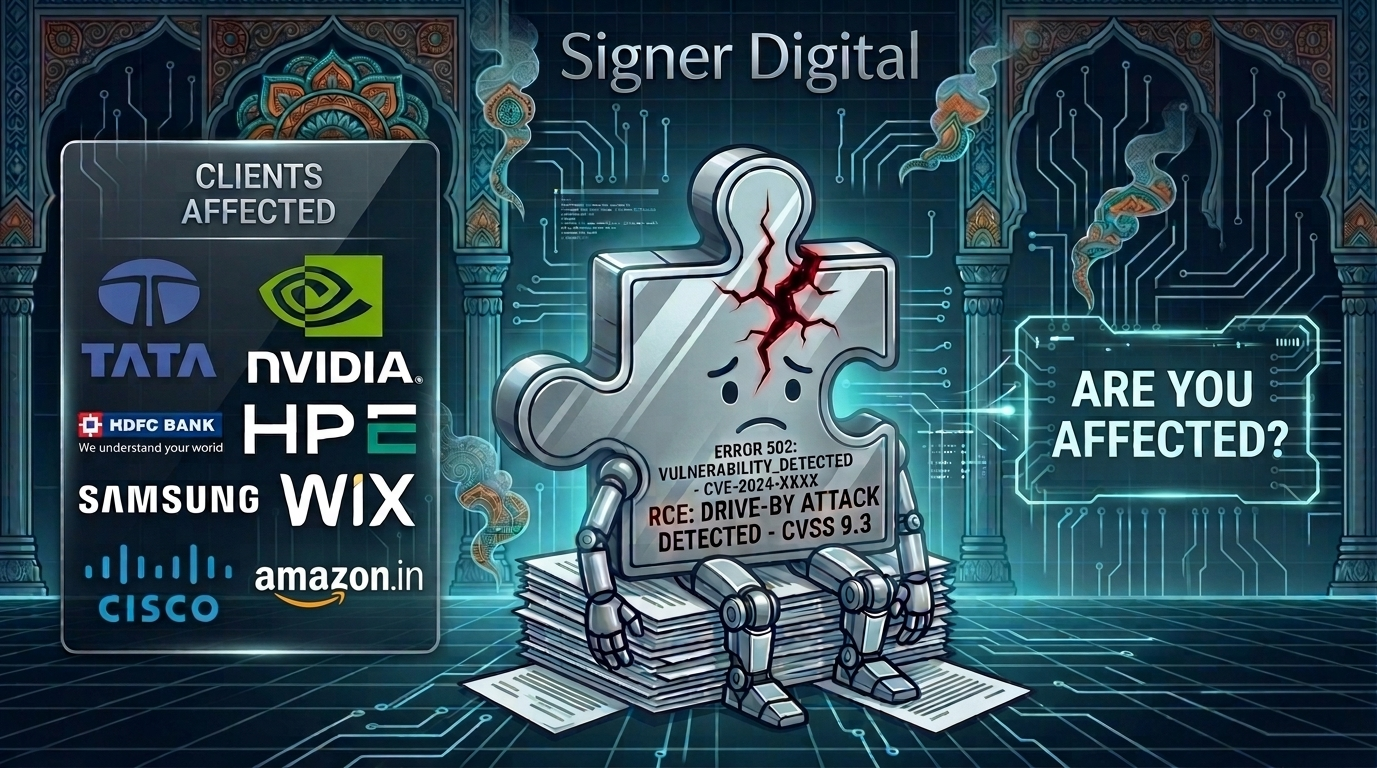
Trusted by NVIDIA, Amazon and Banks, This Extension Let Any Website Run Code on Your PC
Signer.Digital's browser extension and its native helper turned a path-traversal bug into drive-by remote code execution on Windows. Any web page you visited could load an attacker DLL into a process on your machine, then escalate to administrator with a single UAC click.
The Word 'Toad' Gave Any Website Full Control of Chrome's Most Popular VPN
Urban VPN's Chrome extension accepted commands from any website via postMessage with no origin validation. Any page could disconnect your VPN, reroute your traffic, disable security features, and more - silently, with zero user interaction.
The AI Chat Scraping Extension Wall of Shame
We compiled a list of extensions we found scraping AI chats from users or with infrastructure to do so, with none or minimal disclosure.

CRXcavator alternative: how its score worked, and what we built instead
CRXcavator went offline in 2024. Here's how its permission score actually worked, the attacks it was never going to catch, and how Am I Being Pwned reads the code instead.
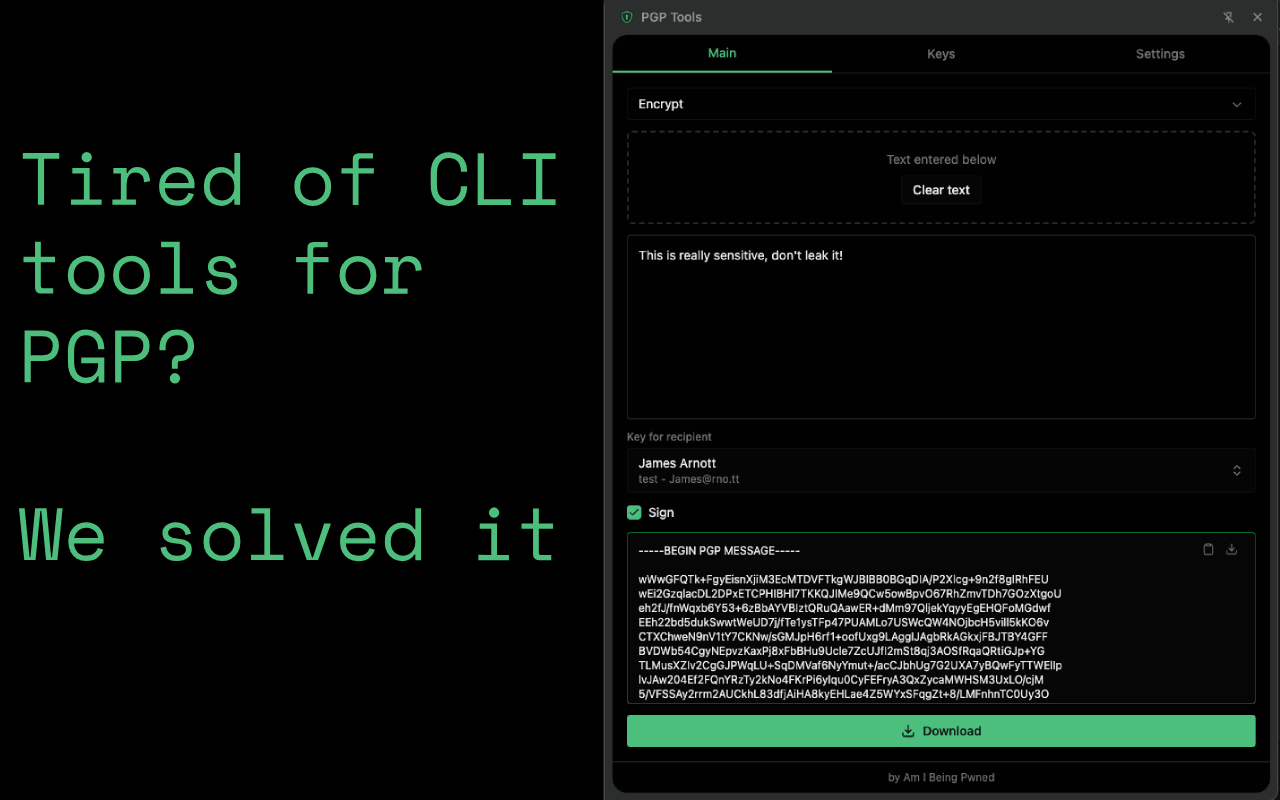
We open-sourced PGP Tools - a browser extension that does PGP properly
We published an open-source PGP browser extension built on Rust/WebAssembly. Private keys stay in WASM memory, passkey unlock via WebAuthn PRF, and the full source is on GitHub.

Am I Being Pwned founder added to Belgium's CCB Wall of Fame
James Arnott, founder of Am I Being Pwned, has been recognised on the Centre for Cybersecurity Belgium's Wall of Fame for responsibly disclosing vulnerabilities through their Coordinated Vulnerability Disclosure Program.

MultiPassword CVSS 8.3 - A password manager that could leak passwords
MultiPassword, a password manager trusted by over 1 million users worldwide, leaked usernames, passwords, URLs and Time-based One Time Passcodes (TOTP) with a low skill attack, in specific but very co

Stylish is Back, Back again!
Stylish, a chrome extension with over 2 million users got called out in 2018 exfiltrating every URL you go to, caught by Robert Heaton in this blog post. He also made a follow up when it came back her